
A Santa Barbara nuclear lab faces a $196,350 federal fine after investigators discovered classified information was processed on unauthorized computer systems.
The National Nuclear Security Administration announced the proposed penalty on Oct. 16 against Mission Support and Test Services, LLC, the contractor operating the Special Technologies Laboratory on Ekwill Street. Federal investigators identified four separate violations during their probe, with one receiving the Department of Energy’s highest severity classification.
That top-tier rating, Severity Level I, is reserved for incidents involving actual harm or significant potential threats to national security. Two additional violations were classified as Severity Level II, with a fourth marked as Severity Level III.
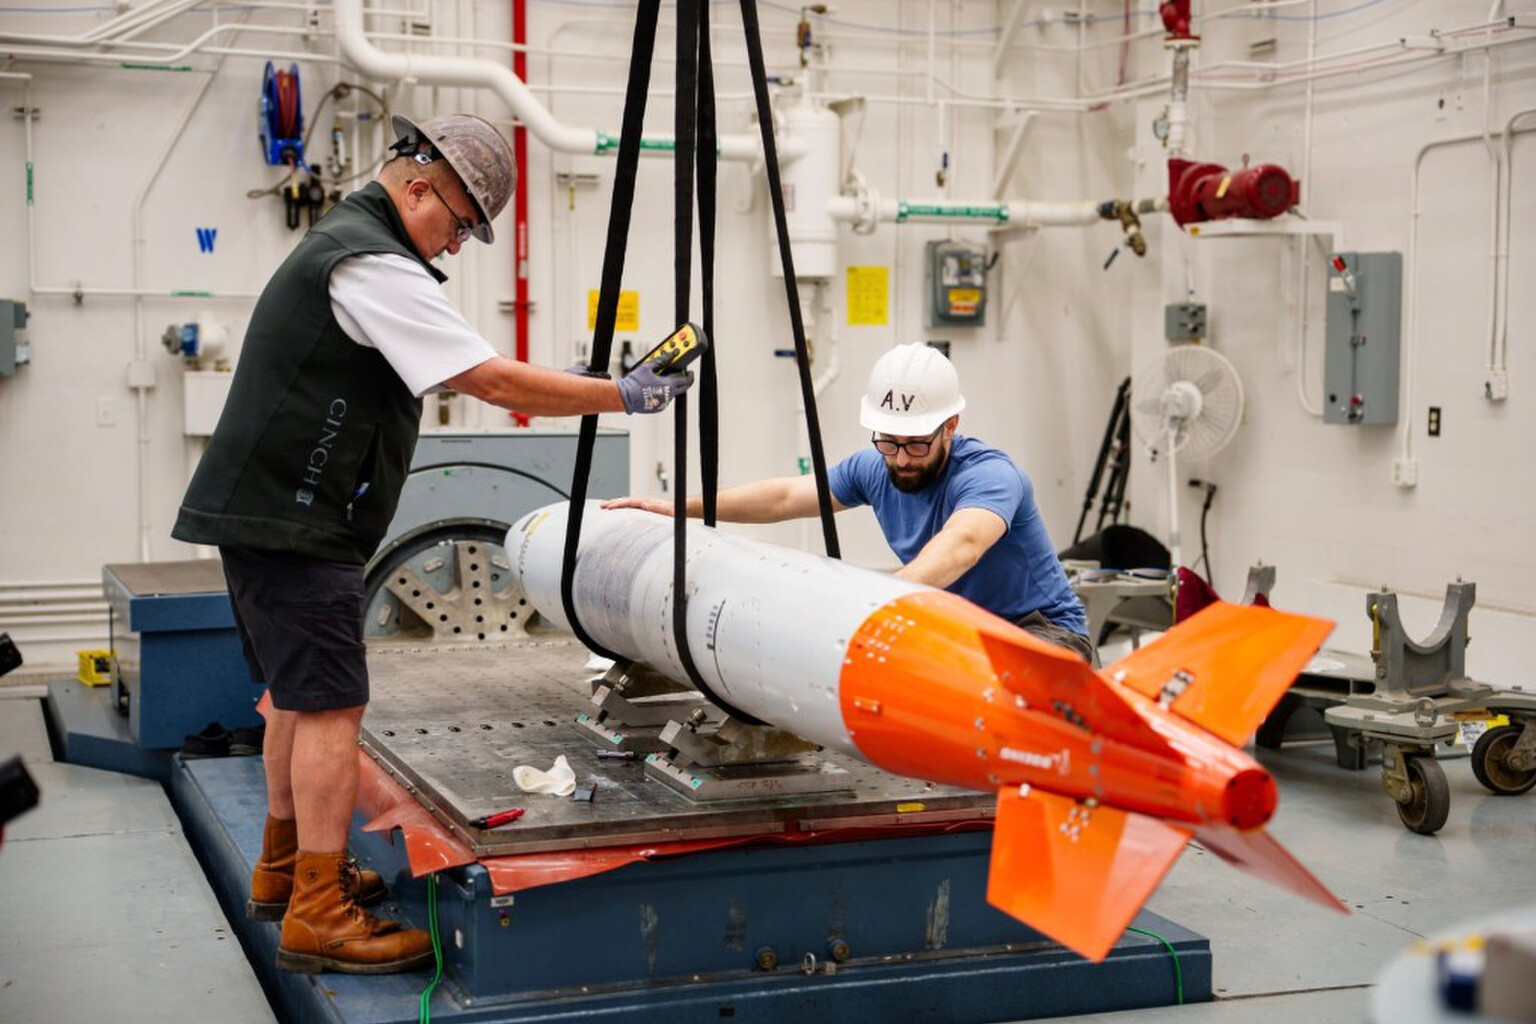
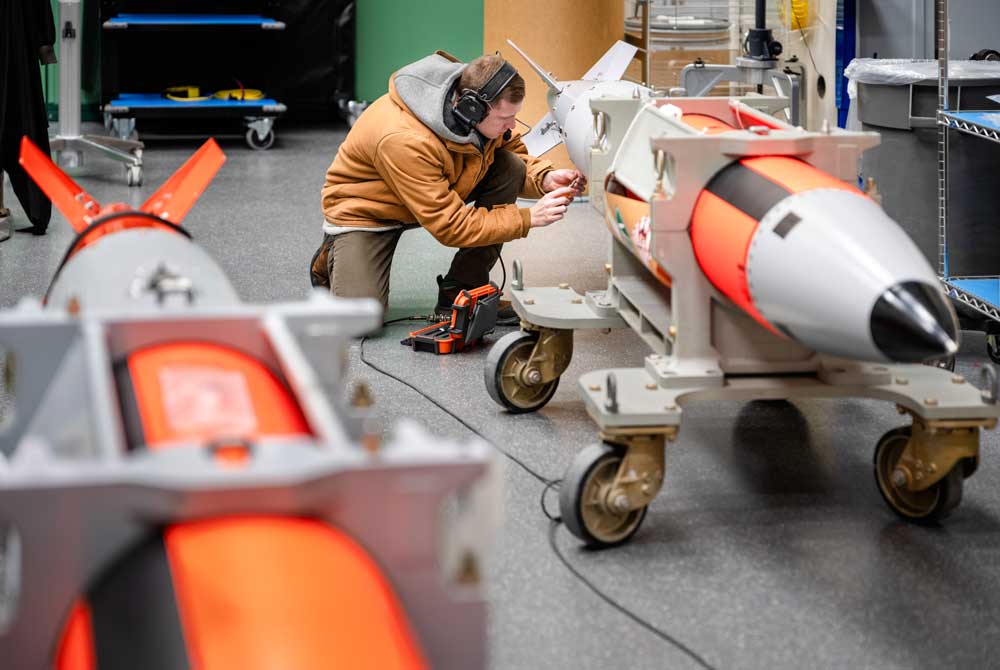
The security failures struck at a facility with a critical mission. The Special Technologies Laboratory develops advanced technologies to assess the safety and reliability of US nuclear weapons. Its scientists and engineers also work on detecting foreign nuclear weapons programs, nuclear counterterrorism, intelligence gathering and cybersecurity. Some projects involve combining artificial intelligence with sophisticated sensors to detect suspicious activity and protect critical infrastructure.
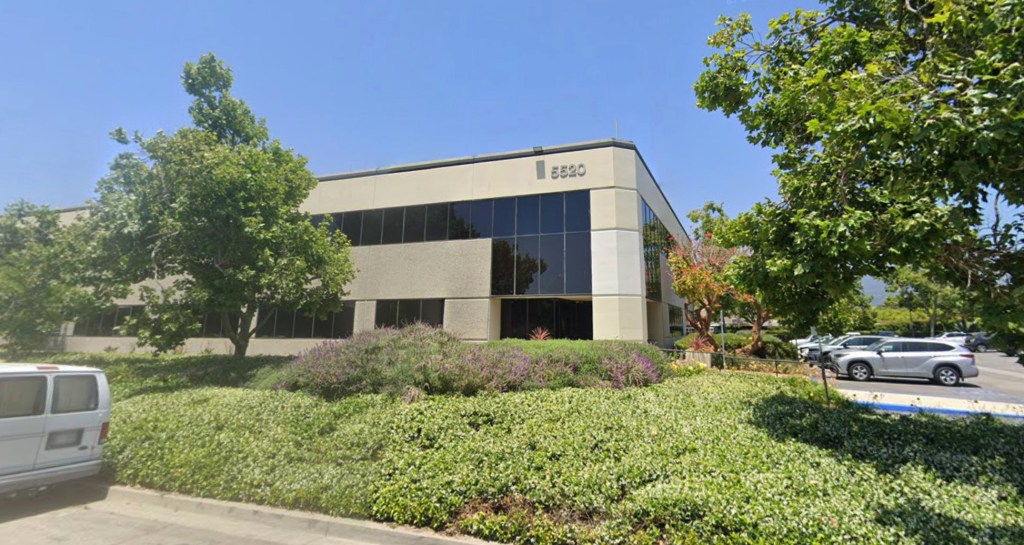
The laboratory operates as part of the Nevada National Security Sites under the NNSA, and has maintained a presence in the Santa Barbara area for more than six decades. In 2023, it co-sponsored the local TechTopia summit, maintaining ties to the region’s technology community.
The incident that sparked the investigation dates back to March 2024. Mission Support and Test Services initially marked the matter as closed in the Energy Department’s security reporting system on Aug. 5, 2024. The contractor later notified the department’s intelligence and counterintelligence office in February 2025, but federal officials continued examining the case.
A Sept. 10 letter to the contractor indicated investigators would also examine whether the incident reflected broader failures to comply with federal security requirements. The department said it would rely on documents collected before and during the site visit, without conducting additional employee interviews or inspections.
Federal security requirements mandate that classified information be handled only on authorized systems with safeguards designed to prevent unauthorized access or disclosure. Using systems that lack those protections can create vulnerabilities, although officials have not established publicly that any classified material was stolen or leaked.
Authorities have not disclosed what specific classified information was mishandled or whether anyone without proper authorization gained access to it. The NNSA’s publicly available summary also does not detail what corrective measures were implemented or whether all security vulnerabilities have been resolved.
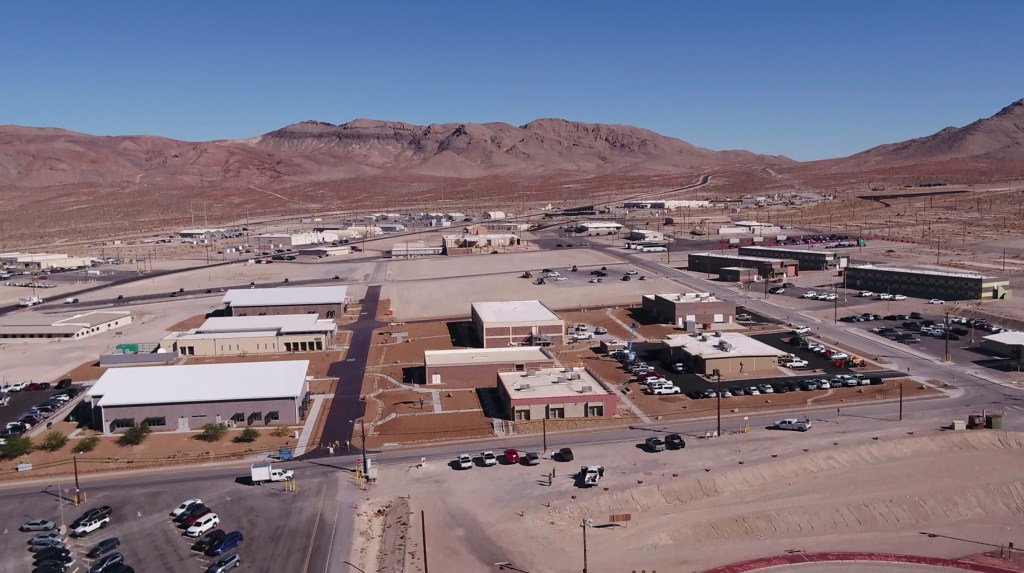
In determining the proposed penalty, federal officials considered the seriousness of the security violations, weaknesses in the contractor’s security program and corrective measures taken to prevent similar incidents.
MSTS can challenge the findings or request a reduction in the financial penalty. Under federal regulations, the contractor generally has 30 calendar days after receiving the notice to respond.
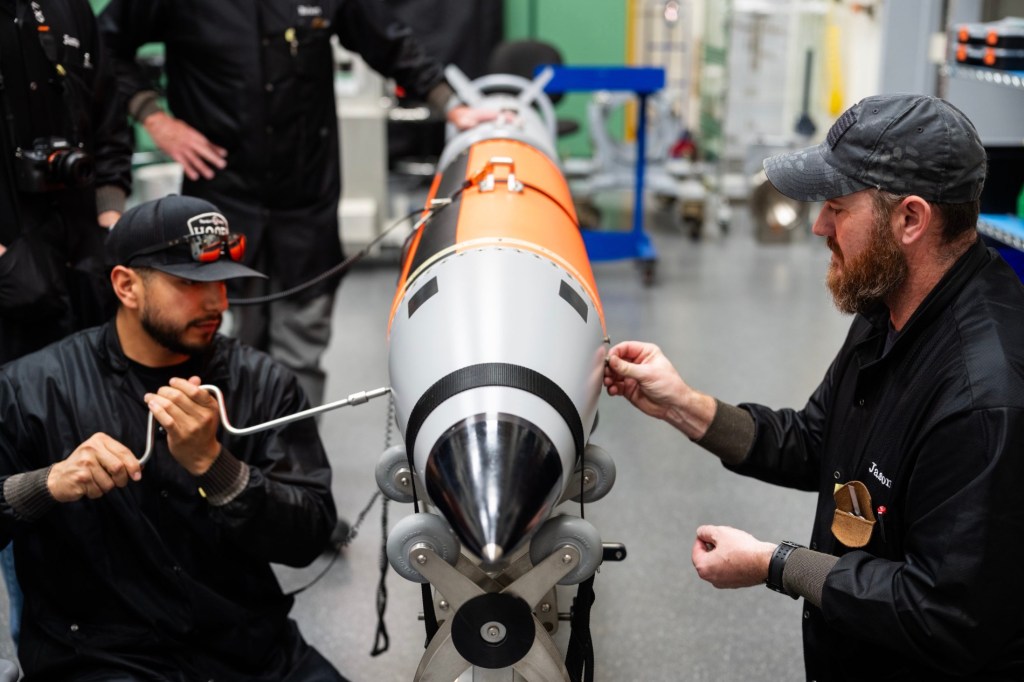
The proposed fine comes as the laboratory continues its work safeguarding America’s nuclear stockpile and monitoring potential nuclear threats abroad. The security failures are particularly concerning given that dual role in both domestic weapons assessment and foreign threat detection.